ARCHITECTURAL PILLAR

AI Agent Safety & Cost

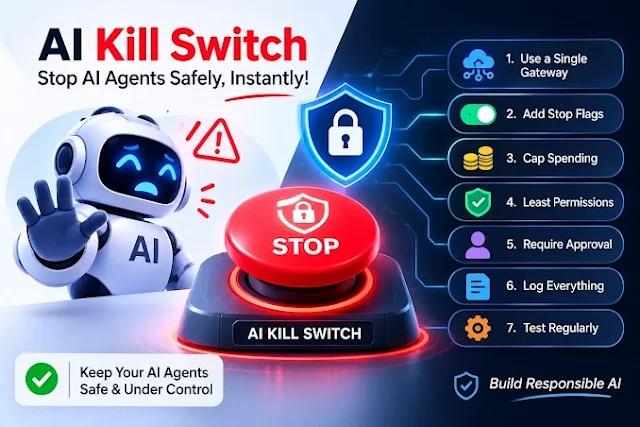
As autonomous AI agents and coding assistants gain direct access to production databases, terminal environments, and external APIs, managing execution safety and controlling operational costs becomes non-negotiable. Unchecked agents can quickly enter infinite retry loops, drain token budgets, hallucinate destructive commands, or introduce dangerous dependency vulnerabilities. This hub provides comprehensive defense-in-depth frameworks for safeguarding production AI deployments. Learn how to implement multi-layered kill switches, deterministic circuit breakers, hard token budget caps, prompt injection firewalls, and human-in-the-loop approval gates via Slack webhooks. We also address cognitive surrender, supply-chain security risks for developer agents, and CERT-In compliance protocols. Protect your infrastructure and balance your ledger with actionable engineering patterns built for resilient enterprise adoption.

11 In-Depth Guides-Last Updated: 2026-11-14
RECOMMENDED STARTING POINT

CrowdStrike Just Launched an AI Kill Switch: How to Build One for Your Own AI Agents

Learn what an AI agent kill switch is and how to build one: stop rules, permissions, spend limits and a safe shutdown path for your own AI agents.

Read Foundation Guide